What you will learn
- Indicate relationships between a group of users and an object. See Modeling User Groups for more. Used here to indicate that all users within a domain can access a document (sharing a document within an organization).
- Model concentric relationship to have a certain relation on an object imply another relation on the same object. See Modeling Concepts: Concentric Relationships for more. Used here is to indicate that writers are also commenters and viewers.
- Using the union operator condition to indicate that a user might have a certain relation with an object if they match any of the criteria indicated. Used here to indicate that a user can be a viewer on a document, or can have the viewer relationship implied through commenter.
- Using the type bound public access in a relationship tuple’s user field to indicate that everyone has a certain relation with an object. See Modeling Public Access for more. Used here to share documents publicly.
- Model parent-child objects to indicate that a user having a relationship with a certain object implies having a relationship with another object in OpenFGA. Used here is to indicate that a writer on a folder is a writer on all documents inside that folder.
Before you start
In order to understand this guide correctly you must be familiar with some OpenFGA concepts and know how to develop the things that we will list below. It would be helpful to have an understanding of some concepts of OpenFGA before you start.OpenFGA concepts
OpenFGA concepts
Modeling concentric relationships
You need to know how to update the authorization model to allow having nested relations such as all writers are readers. Learn more →Modeling object-to-object relationships
You need to know how to create relationships between objects and how that might affect a user’s relationships to those objects. Learn more →Used here to indicate that users who have access to view a folder have access to view all documents inside it.Modeling public access
You need to know how to add a relationship tuple to indicate that a resource is publicly available. Learn more →Concepts & configuration language
What you will be modeling
Google Drive is a system to store, share, and collaborate on files and folders. Source In this tutorial, you will build a subset of the Google Drive permission model (detailed below) in OpenFGA, using some scenarios to validate the model.Note: For brevity, this tutorial will not model all of Google Drive’s permissions. Instead, it will focus on modeling for the scenarios outlined below
Requirements
Google Drive’s permission model is represented in their documentation. In this tutorial, you will be focusing on a subset of these permissions. Requirements:- Users can be owners, editors, commenters and viewers of documents
- Documents can be shared with all users in a domain
- Folders can contain documents and users with a certain permission on a folder have that same permission to a document in that folder
- Documents and folders can be shared publicly
Defined scenarios
There will be the following users:- Anne, who is in the xyz domain
- Beth, who is in the xyz domain
- Charles, who is in the xyz domain
- Diane, who is NOT in the xyz domain
- Erik, who is NOT in the xyz domain
- a 2021-budget document, owned by Anne, shared for commenting with Beth and viewable by all members of the xyz domain.
- a 2021-planning folder, viewable by Diane and contains the 2021-budget document
- a 2021-public-roadmap document, owned by Anne, available for members xyz domain to comment on and is publicly viewable
Modeling Google Drive’s permissions
01. Individual permissions
To keep thing simple and focus on OpenFGA features rather than Google Drive complexity we will model only four roles (Viewer, Commenter, Writer, Owner). At the end of this section we want to have the following permissions represented:
The snippet above indicates that objects of type document have users related to them as “viewer” if those users belong to the userset of all users related to the document as “viewer”.This means that a user can be directly related as a viewer to an object of type “document”
beth is a commenter of document:2021-budget we create this relationship tuple:
We can now ask OpenFGA “is beth a commenter of repository document:2021-budget?”
We could also say that anne is an owner of the same document:
And ask some questions to OpenFGA:
The first reply makes sense but the second one does not. Intuitively, if anne was an owner, she was also be a writer. In fact, Google Drive explains this in their documentation

Let’s examine one of those relations in detail:objects of type document have users related to them as “viewer”: if they belong to any of (the union of) the following:
- the userset of all users related to the document as “viewer”
- the userset of all users related to the document as “commenter”
02. Organization permissions
Google Drive allows you to share a file with everyone in your organization as a viewer, commenter or writer/editor.

Objects of type “domain” have users related to them as “member” if they belong to the userset of all users related to the domain as “member”.In other words, users can be direct members of a domain.
03. Folder permission propagation
Permission propagation happens between folders and files: if you are a viewer in a folder, you can view its documents. This applies even when you are not explicitly a viewer in a document.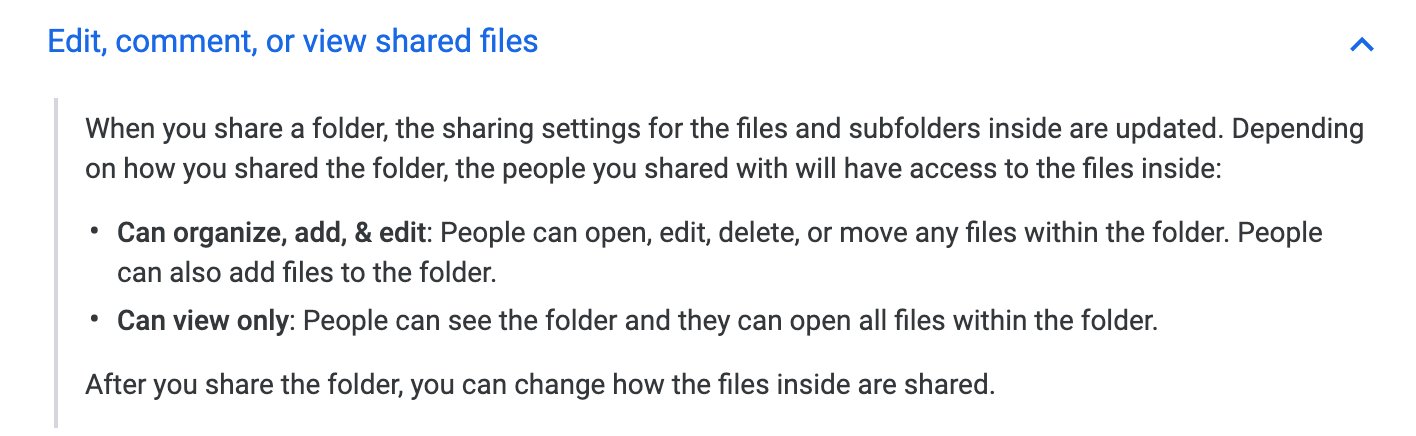 At the end of this section we want to end up with the following permissions represented. Note that a folder is an object in the document type, as we do not need a separate type:

Notice the newly added “parent” relation in the configuration above.
- [done] they have a viewer relationship (directly or through domain membership)
- [pending] they have a viewer relationship with the parent document
The users with a viewer relationship to a certain object of type “document” are any of:
- the “viewers”: the set of users who are directly related to the document as a “viewer”
- the “commenters”: the set of users who are related to the object as “commenter”
- the “viewers of the parents”: from the objects who are related to the doc as parent, return the sets of users who are related to those objects as “viewer”
- read all relationship tuples related to document:2021-budget as parent which returns:
[{ "object": "document:2021-budget", "relation": "parent", "user": "document:2021-planning" }]- for each relationship tuple read, return all usersets that match the following, returning tuples of shape:
{ "object": "document:2021-planning", "viewer", "user": ??? }including: { "object": "document:2021-planning", "viewer", "user": "user:diane" }04. Sharing files and folders publicly
Google Drive has a feature which allows sharing a file or folder publicly, and specifying the permissions a public user might have (writer/commenter/viewer). Assume thatAnne has created a new document: 2021-public-roadmap, has shared it with commenter permissions to the xyz.com, and has shared it as view only with the public at large.

user for viewer relation.
To mark Anne as the owner, the domain members as commenters and the public as viewers, we need to add the following relationship tuples:
Anne is an owner of the document
Beth is a member of the xyz.com domain, and so can comment but cannot write
Erik is NOT a member of the xyz.com domain, and so can only view the document
Related Sections
Take a look at the following sections for more information.Search with permissions
Give your users search results with objects that they have access to