What is a userset?
A userset represents a set or collection of users. Usersets can be used to indicate that a group of users in the system have a certain relation with an object. This can be used to assign permissions to groups of users rather than specific ones, allowing us to represent the permissions in our system using less tuples and granting us flexibility in granting or denying access in bulk. In OpenFGA, usersets are represented via this notation:object#relation, where object is made up of a type and an object identifier. For example:
company:xyz#employeerepresents all users that are related tocompany:xyzasemployeetweet:12345#viewerrepresents all users that are related totweet:12345asviewer
How do check requests work with usersets?
Imagine the following authorization model: Now let us assume that the store has the following tuples:- Userset “Members of the xyz org” can read the budget document
- Anne is part of the userset “Members of the xyz org”
anne has a reader relationship with document:budget, OpenFGA will check whether anne is part of the userset that does have a reader relationship. Because she is part of that userset, the request will return true:
How do expand requests work with usersets?
Imagine the following authorization model: If we wanted to see which users and usersets have areader relationship with document:budget, we can call the Expand API. The response will contain a userset tree where the leaf nodes are specific user IDs and usersets. For example:
Internals
Using the type definitions in the authorization model, some of the situations we can represent are:- that a user is not in a set of users having a certain relation to an object, even if a relationship tuple exists in the system. See Disabling Direct Relationships
- that a user has a certain relationship with an object if they are in the union, intersection or exclusion of usersets.
- that a user being in a set of users having a certain relation to an object can result in them having another relation to the object. See Concentric Relationships
- that the user being in a set of users having a certain relation to an object and that object is in a set of users having a certain relation to another object, can imply that the original user has a certain relationship to the final object. See Object-to-Object Relationships
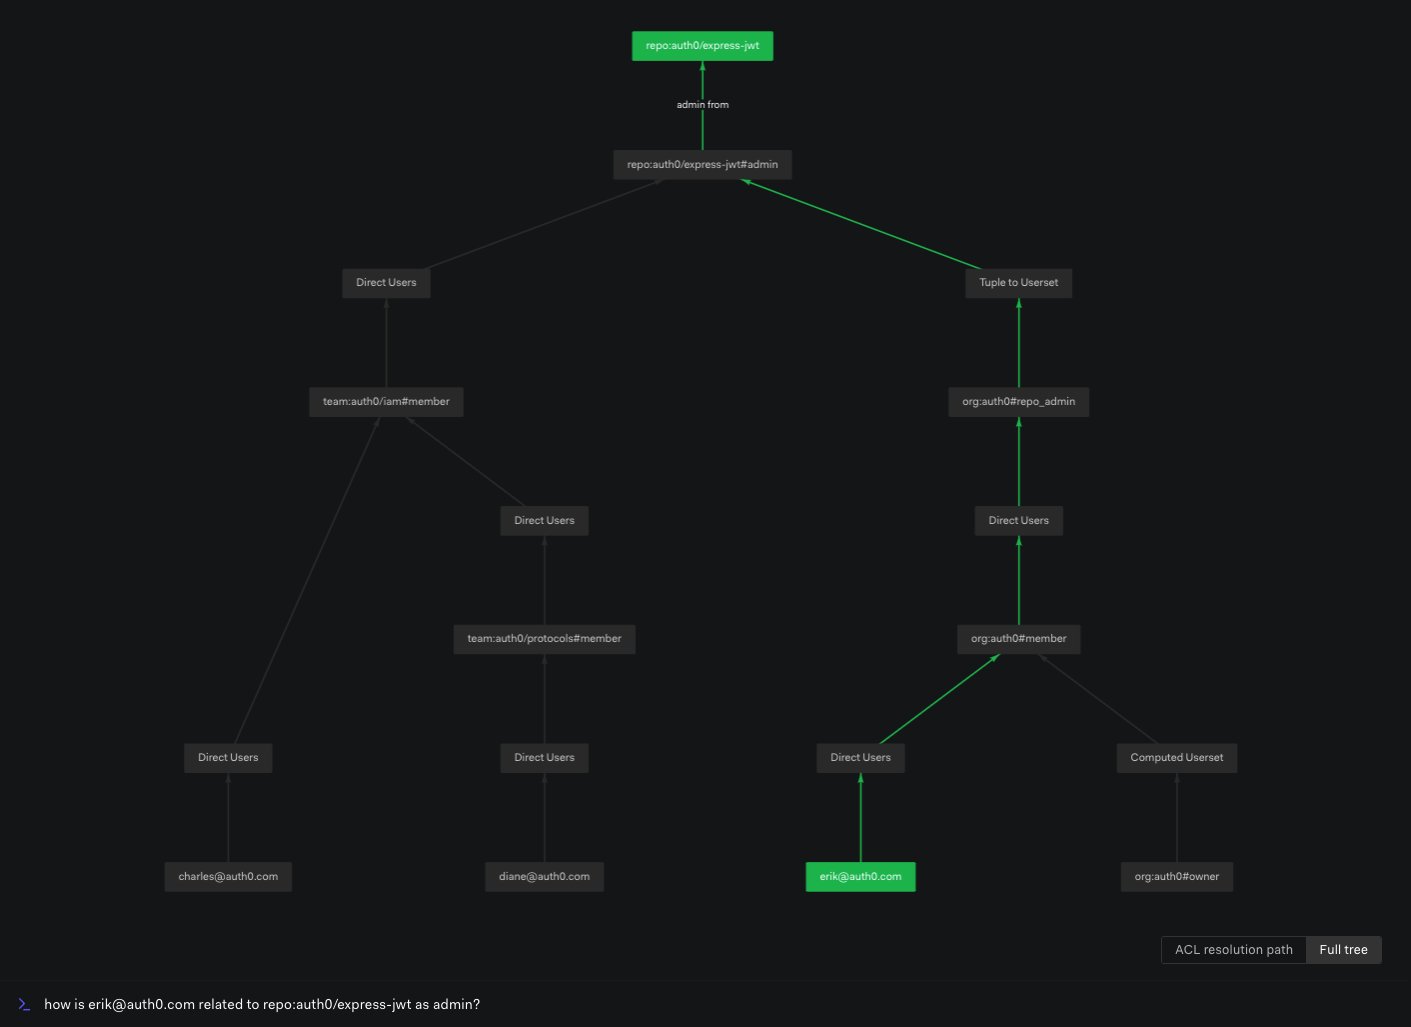
check(user, relation, object), OpenFGA will perform the following steps:
- In the authorization model, look up
typeand itsrelation. Start building a tree where the root node will be the definition of thatrelation, which can be a union, exclusion, or intersection of usersets, or it can be direct users. - Expand all the usersets involved into new nodes in the tree. This means recursively finding all the users that are members of the usersets. If there are direct relationships with users, create leaf nodes.
- Check whether
useris a leaf node in the tree. If the API finds one match, it will return immediately and will not expand the remaining nodes.
Related Sections
See the following sections for more information:Managing Group Membership
How to add users to a userset
Managing Group Access
How to add permissions to a userset